
Online training · Module 2 of 3 · Registration open
NASU invites insurance market professionals to an online training on the EU framework for digital operational resilience, held within the international cooperation programme STEP IN 2 EU. Five days “from fundamentals to practice” – from the logic of the Regulation to an implementation roadmap for a Ukrainian insurer.
7–11 December 2026
10:00–14:00 Kyiv time
Zoom
Ukrainian interpretation
free of charge
Open to all insurance market participants, regardless of NASU membership
Digital
Operational
Resilience
Act

duration
5 days
7 to 11 December 2026, Monday to Friday
time
10:00–14:00
Kyiv time + self-study of the materials
platform
Zoom
a personal link is sent to your e-mail after registration
language
EN → UA
lectures in English with simultaneous interpretation into Ukrainian
certificate
Certificate
NASU certificate for at least 80% attendance
price
Free
all participants receive the module materials
// why_dora
Until recently, EU requirements on cyber security and IT were scattered. Regulation (EU) 2022/2554 brought them together in a single binding standard: a financial entity must treat digital and operational risks as seriously as financial ones. DORA rests on five pillars:
nasu@step-in-2-eu: ~/dora
$ dora --scope insurers
# Regulation (EU) 2022/2554 · applies since 17.01.2025
[01] ICT risk management
art. 5–16
[02] Incident reporting
art. 17–23
[03] Resilience testing
art. 24–27
[04] ICT third-party risk
art. 28–44
[05] Information sharing
art. 45
$ nasu train --days 5
01
Protection, threat detection, response and recovery under the responsibility of the management body.
Art. 5–16
02
Classifying incidents and notifying the supervisor of major ones within set deadlines.
Art. 17–23
03
From vulnerability scanning to threat-led penetration testing (TLPT).
Art. 24–27
04
Cloud services, software, outsourcing: contractual terms, register of information, exit strategies.
Art. 28–44
05
Sharing information on cyber threats and vulnerabilities among financial entities.
Art. 45
For Ukrainian insurers DORA is the target model on the path to EU integration. The topic is new for most companies, so the module starts from the fundamentals.
// program
Day one builds a common understanding of the topic, the following days go deeper into individual pillars, and the final day closes with an implementation roadmap. Daily from 10:00 to 14:00, ending with a Q&A session.
The training is delivered by experts from zeb.consulting (Germany) in English with simultaneous interpretation into Ukrainian.
DAY_01
07
December · Monday
Art. 1–4 · NIS2
What digital operational resilience means and why it has become a regulatory priority: insurers’ dependence on IT, cloud services, outsourcing and cyber attacks on the financial sector. The five pillars of the Regulation, its scope and the proportionality principle, the link with the company’s governance system and the relationship with NIS2.
DAY_02
08
December · Tuesday
Art. 5–16
Role and responsibility of the management body. Register of ICT assets and their criticality; protection, detection, response and recovery; the ICT business continuity and recovery plan; periodic review of the framework.
DAY_03
09
December · Wednesday
Art. 17–23 · 2024/1772 · 2025/301
Criteria and thresholds for a major incident: clients and counterparts, duration and downtime, geographical spread, data losses, economic impact, criticality of services. Typical classification errors, the difference between a major incident and a significant cyber threat, deadlines and content of the initial, intermediate and final reports.
4h
initial notification – after the incident is classified as major (no later than 24 h after becoming aware of it)
72h
intermediate report – after the initial notification
1M
final report – after the latest intermediate report
Art. 19 of Regulation (EU) 2022/2554; Art. 5 of Delegated Regulation (EU) 2025/301
DAY_04
10
December · Thursday
Art. 24–27 · TIBER-EU
From the basic level (vulnerability scanning, security assessments) to threat-led penetration testing. The TIBER-EU methodology: team roles, threat intelligence, testing phases. Who must undergo TLPT and how often.
DAY_05
11
December · Friday
Art. 28–45 · roadmap
Mandatory contractual terms with ICT providers, the register of information on ICT services, critical or important functions. Concentration risk of cloud providers, substitutability and exit strategies. Oversight of critical ICT third-party providers, threat information sharing. A practical DORA implementation roadmap.
The order of topics and the distribution of material between days are indicative and may be adjusted. The overall content and scope of the module remain unchanged.
// speakers
The programme is delivered by experts from zeb, a leading European management consultancy specialising in financial services. Both experts will contribute throughout the week, alternating by topic; some sessions may be delivered by colleagues from their teams.
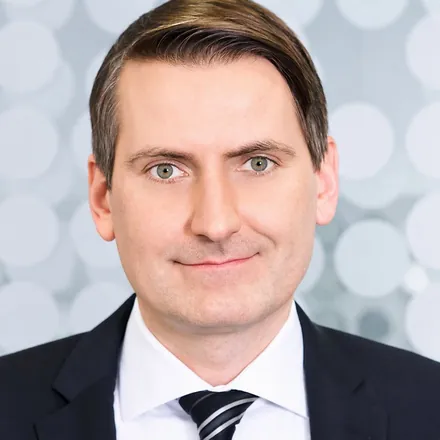
$ whoami
Partner, zeb
Advises banks and other financial institutions on ICT governance, outsourcing, operational resilience and regulatory transformation. His project experience includes implementing COBIT-based IT governance frameworks, reorganising outsourcing management functions and developing governance, risk and compliance processes – all closely relevant to DORA. With zeb since 2009, he specialises in organisational transformation, operational excellence and regulatory implementation.
Education: doctorate in Finance (Goethe University Frankfurt), degree in Business Administration (University of Bayreuth), studies in International Business (Helsinki School of Economics).
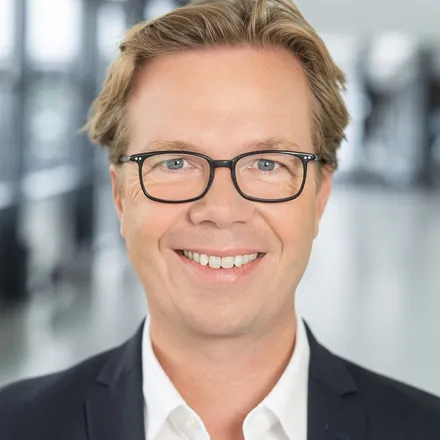
$ whoami
Expert Partner, zeb
Advises global systemically important banks and major European financial institutions on complex strategic, organisational and transformational challenges. With zeb since 1999 and a Partner since 2009. Since 2022 he has headed the zeb.business school, where he is active as a coach, trainer and lecturer.
Education: Business Administration and Commerce (University of Paderborn; Melbourne Mt. Eliza Business School, Australia), PhD in Banking and Finance (University of Paderborn) with a focus on ALM and Treasury Management. Former Adjunct Professor of Banking and Finance at RMIT University, Australia.
Language of instruction: English, with simultaneous interpretation into Ukrainian.
// how_it_works
01
Fill in a short form – participation is free. The completed form is your application to take part.
02
A personal Zoom link and the materials are sent to the e-mail you give at registration.
03
Five webinars from 10:00 to 14:00 in English with simultaneous interpretation into Ukrainian. Each day ends with a Q&A session.
04
Self-study of the module materials, which all participants receive.
05
NASU certificate for at least 80% attendance. There is no knowledge test.
Important: please give your correct work e-mail at registration – attendance is recorded and the certificate is issued against it.
// audience
chief information security officers (CISO)
risk managers
IT managers
business continuity specialists
internal audit
compliance
management board members
supervisory board members
DORA makes digital resilience a direct responsibility of the management body, so the training is also useful for company executives. If your company has no separate CISO or risk manager position, we welcome the specialists who perform these functions alongside other duties or are responsible for IT and business continuity.
The training is open to all insurance market participants regardless of NASU membership.
// legal_basis
DORA
Regulation (EU) 2022/2554, applicable from 17 January 2025
↗
Directive
Directive (EU) 2022/2556 (accompanying directive)
↗
RTS 2024/1772
criteria for classifying ICT-related incidents
↗
RTS 2025/301
content and time limits of major incident reports
↗
TIBER-EU
threat intelligence-based ethical red teaming framework
↗
Links lead to the official texts on EUR-Lex and to the ECB page on TIBER-EU.
// modules[3]
Module 2 · 7–11 December 2026 · registration open
You are on this module’s page.
Module 3 · 25–29 January 2027
The updated solvency regime for insurers.
DORA
Participation is free of charge. The Zoom link and the materials will be sent to your work e-mail.
The international cooperation programme STEP IN 2 EU is co-financed by the governments of Germany and Norway, the European Union under the EU4Business initiative, as well as the governments of Lithuania and Estonia. The programme is implemented by Deutsche Gesellschaft für Internationale Zusammenarbeit (GIZ) GmbH.